
Front pageRansomware & Data Breaches
Maersk Discloses Unauthorized Access to Legacy System Amid Ransomware Claim
Maersk reports a breach of a legacy system from a prior acquisition, with ransomware group WhiteArmor alleging data theft and demanding a $5 million ransom.
- Filed
- Read
- 2 min read
Maersk announced on 11 November 2026 that an unauthorized party accessed a local legacy system inherited from a previous acquisition. The company emphasized that the breach is confined to that isolated environment and has not affected its broader network, customer‑facing platforms or partner integrations.
Scope of the incident
The intrusion involved extraction of data from the legacy system, but Maersk stated that its findings so far strongly suggest that no sensitive data has been disclosed. Operational services, including the widely used booking portals, remain functional, and the firm does not expect any disruption to its logistics operations.
Ransomware claim
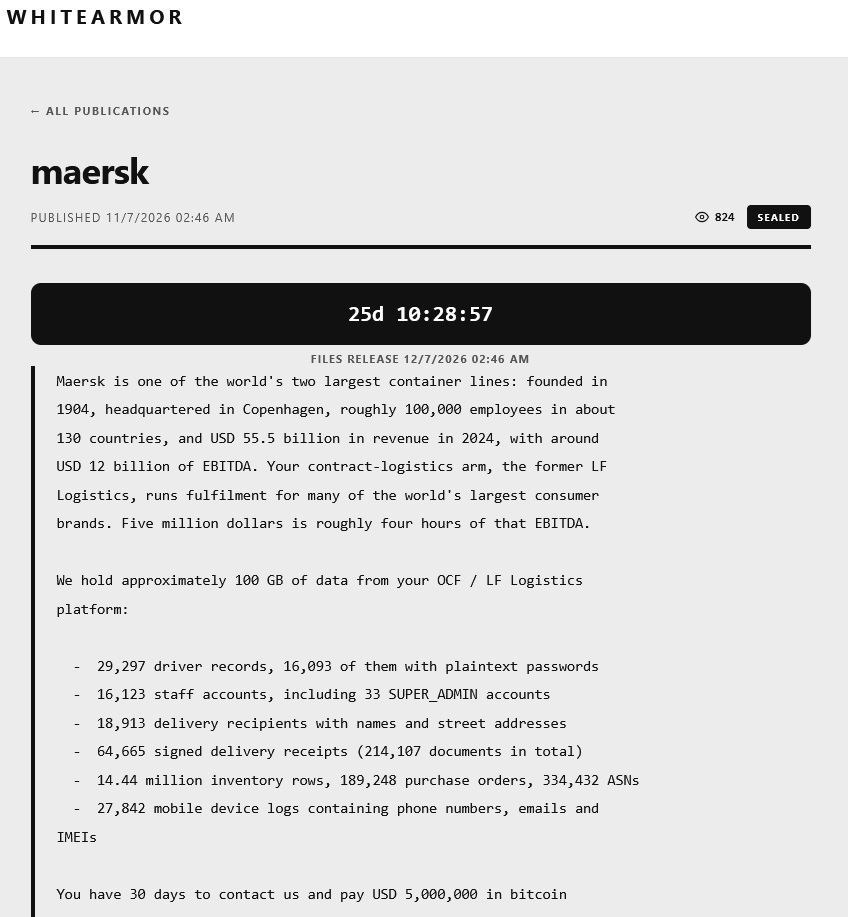
The group identifying itself as WhiteArmor has claimed responsibility for the breach. Attackers allege they stole roughly 100 GB of data, citing driver records, plaintext passwords, admin accounts, delivery receipts, inventory rows and mobile device logs, and have set a 30‑day deadline for a $5 million bitcoin ransom.
These figures and data categories originate from the threat actor's claims and have not been independently verified or confirmed by Maersk.
Investigation and response
Maersk has launched a full investigation, which remains ongoing, to determine the exact timeline, the specific system compromised and the volume of data actually exfiltrated. The company has not confirmed the ransomware group’s allegations and continues to assess the situation.
Why it matters
Although the breach is limited to a single legacy environment, the alleged exposure of credentials and operational records could pose downstream risks for customers and partners who rely on Maersk’s shipping and logistics platforms. Even without confirmed disclosure of sensitive data, the incident highlights the challenges of integrating legacy assets from acquisitions and the importance of securing them against modern threat actors.
Context and next steps
Maersk’s statement underscores that the incident does not impact its core services, but the ongoing investigation aims to clarify the extent of any data loss and to implement remediation measures. Stakeholders are watching for further updates that may detail any additional security controls or notifications required under data‑protection regulations.
Sources
Sources
Keep reading
Spanish Police Arrest Suspect in Probe Into AI-Assisted Cyber Intrusions Targeting Public Services
A suspect was arrested in Ciudad Real for allegedly using AI tools to hack municipal and private platforms, raising concerns over emerging cyber‑threats.
South Korean Companies Hit by Leak of Anthropic Claude Account Data
Personal details of over a hundred South Korean corporate Claude users were exposed after an unauthorized party accessed Anthropic’s system, prompting a privacy investigation.
AI‑driven BOSSAI mesh attacks emergency services, universities and banks across 11 nations
A lone operator deployed a network of 12 AI agents to breach emergency‑service providers in Taiwan, Thai universities and Mexican banks, stealing medical and personal data.