
Front pageCyber Attacks & Incidents
Optimizely Supply-Chain Attack Turned Trusted Website Scripts Into Malware Delivery Channels Across 178 Organisations
Visitors to affected sites on 16 November could have faced card skimming, crypto-wallet address swaps and iPhone exploit kits; Optimizely says the flaw is fixed.
- Filed
- Read
- 3 min read
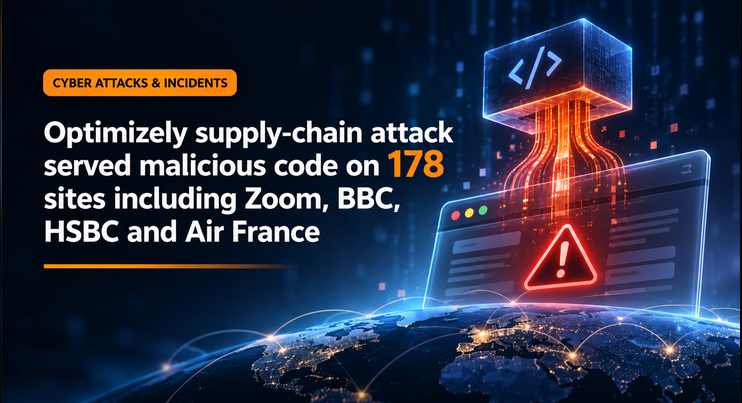
A vulnerability in Optimizely's Web Experimentation platform gave attackers a way to inject malicious JavaScript into customer projects, turning a widely trusted website service into a delivery channel for malware. Visitors to websites belonging to at least 178 organisations were exposed, including those of Zoom, the BBC, CNN, Salesforce, GitLab, HSBC and Air France-KLM.
Security firm Report URI identified 188 infected Optimizely scripts associated with the organisations on 16 November 2026. Rather than compromising each company's infrastructure individually, attackers exploited a weakness in a shared service to reach visitors through scripts already embedded in those websites.
How the attack unfolded
According to Optimizely's incident report, the attackers exploited a vulnerability in the Web Experimentation account signup flow and used it to inject malicious JavaScript into customer projects.
The compromised scripts were delivered through Optimizely's legitimate infrastructure, making the malicious code appear to be part of the normal website functionality. This allowed the attackers to exploit the trust organisations had placed in an external service without needing to breach each customer's own servers.
Report URI's investigation identified a multi-purpose malicious toolkit. Its capabilities included replacing cryptocurrency wallet addresses with attacker-controlled alternatives, intercepting payment-card details entered into vulnerable website forms, and collecting browser cookies and screenshots under specific conditions.
The campaign also incorporated two iOS exploit kits, Coruna and DarkSword, delivered to visitors using vulnerable iPhones and iPads. These components targeted older iOS versions rather than indiscriminately compromising every Apple device.
The cryptocurrency theft was confirmed through transactions traced to attacker-controlled wallets. Report URI estimated that approximately $7,040 had reached those wallets during the observed campaign. However, the researchers could not establish how many payment-card details or cookies had actually been exfiltrated.
Major brands among those exposed
The affected organisations spanned technology, media, finance, retail and travel. Zoom, the BBC, CNN, Salesforce, GitLab, IKEA, HSBC, Equifax, Air France-KLM, Ledger and Peacock were among the names identified by Report URI.
The presence of malicious code on a website does not, by itself, establish that every visitor suffered a compromise. The actual impact depended on whether the script executed, whether the visitor's activity triggered a particular payload and whether the targeted device was vulnerable.
Payment-card exposure also had limitations. Report URI explained that cards entered into hosted payment iframes, including those provided by Stripe and Adyen, were outside the reach of the recovered card-skimming functionality. Payment details entered directly into affected website forms were potentially exposed.
For the iOS component, Apple confirmed that the vulnerabilities targeted by the exploit kits had already been addressed in software updates released previously. Devices running updated software were therefore protected against those vulnerabilities.
Optimizely's response
Optimizely published an incident report on 17 November, outlining the vulnerability and its response.
The company said it had blocked access to the vulnerable signup flow, deployed a fix, removed injected code from affected projects, revoked tokens and terminated active sessions. It also reset access for affected accounts and engaged Mandiant to assist with the forensic investigation.
Its reported incident timeline placed the first malicious code injection at 07:51 UTC on 16 November. The company identified the activity at 13:34 UTC and deployed a fix at 16:10 UTC. Active sessions were subsequently terminated, tokens revoked and malicious code removed from affected projects.
The company also clarified that the incident concerned its Web Experimentation product.
A wider warning about third-party dependencies
The incident exposes a weakness that extends beyond Optimizely. Organisations routinely embed external scripts for analytics, advertising, experimentation and personalisation, often granting them access to sensitive pages and browser activity.
When one of these suppliers becomes compromised, the consequences can spread across otherwise unrelated organisations. The companies involved may have maintained their own security controls, yet still deliver malicious code through an integration they trusted.
For security teams, third-party JavaScript should be treated as an actively monitored dependency rather than a permanently trusted component. Maintaining an inventory of external scripts, monitoring unexpected changes, restricting unnecessary script execution and enforcing carefully designed Content Security Policies can help reduce exposure.
The Optimizely incident is a reminder that securing an organisation's own infrastructure is only part of the job. The code delivered to customers' browsers through external services deserves equal scrutiny.
Sources
- Report URI – Original technical investigation
- Optimizely – Official security incident report (17 November 2026)
- Reuters
- The Record
- Ars Technica
This brief was prepared with AI assistance from the sources above and reviewed by our editors.
Sources
Keep reading

CISA Warns Critical Puppet Enterprise Flaw (CVE-2026-115731) Is Being Exploited, Sets 1 December Deadline
The deserialization bug in report handling scores 9.4 under CVSS 4.0 and can let a client with a signed agent certificate run code on the Puppet server.

South Korea's Yellow Umbrella Data Breach Exposes Information of 362,000 Members
The operator says an outside investigation found almost one in five members affected, up from about 205,000; names, partial ID numbers and contribution amounts were exposed.
Cyberattack Disrupts Hospital Clínico Universidad de Chile Systems as Lawmakers Demand Answers
A cyberattack forced the Chilean hospital’s booking website and call centre offline, sparking urgent oversight letters and fears over patient record safety.